Enterprise Vulnerability Scanning & Risk Mitigation
A comprehensive infrastructure audit uncovering critical misconfigurations and implementing zero-trust policies.
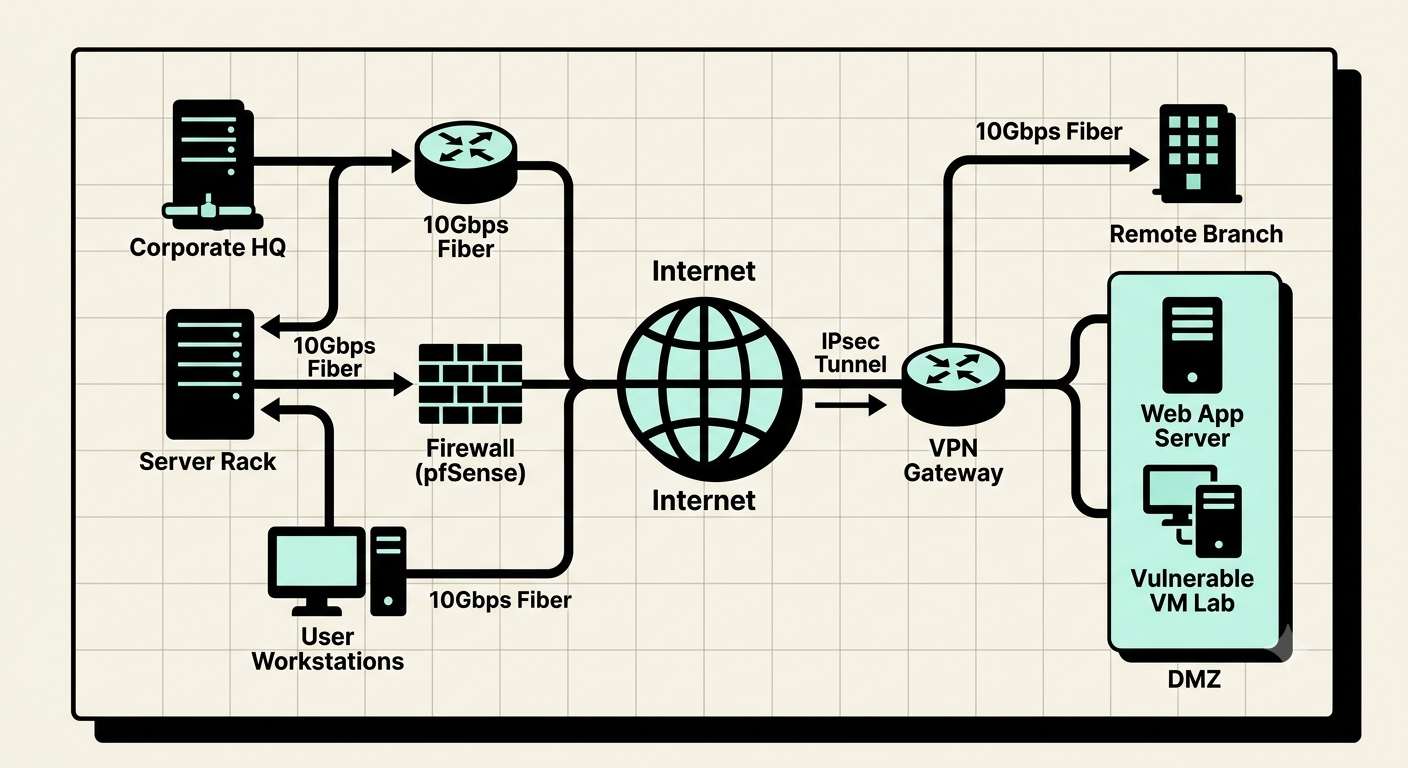
Role
Lead Security Analyst
Timeline
3 Weeks
The Outcome
Reduced attack surface by 45% and successfully patched 3 critical CVEs before deployment.
The Challenge
The client, a mid-sized financial services firm, was migrating their legacy on-premise infrastructure to a hybrid cloud environment. During this transition, visibility into endpoint security dropped, leading to potential unpatched vulnerabilities across their new Active Directory forest.
The Approach
I initiated a grey-box penetration test. First, I mapped the external attack surface using Nmap and Amass. Next, I ran authenticated vulnerability scans utilizing Nessus to identify misconfigurations in the internal routing tables.
- Conducted OSINT to identify exposed credentials.
- Executed privilege escalation tactics in a sandboxed environment to prove impact.
- Audited the AWS IAM roles for excessive permissions.
Key Finding:
Discovered an unauthenticated SMB share containing backup configuration files, which allowed direct access to firewall rules.
Results & Remediation
Delivered a comprehensive 40-page executive and technical report. The engineering team immediately restricted SMB access and implemented a strict Zero-Trust Network Access (ZTNA) policy. Overall security posture score improved from C- to A within 30 days.