Forest is a fantastic Active Directory machine on HackTheBox that tests your knowledge of Windows enumeration, Kerberos misconfigurations, and AD mapping.
1. Initial Enumeration
We start with a standard Nmap scan against the target IP. Seeing ports 88 (Kerberos), 389 (LDAP), and 445 (SMB) immediately screams Domain Controller.
$ nmap -sC -sV -p- 10.10.10.161
Using enum4linux, we can dump the domain user list. This gives us a solid foundation for our next step: AS-REP Roasting.
2. AS-REP Roasting
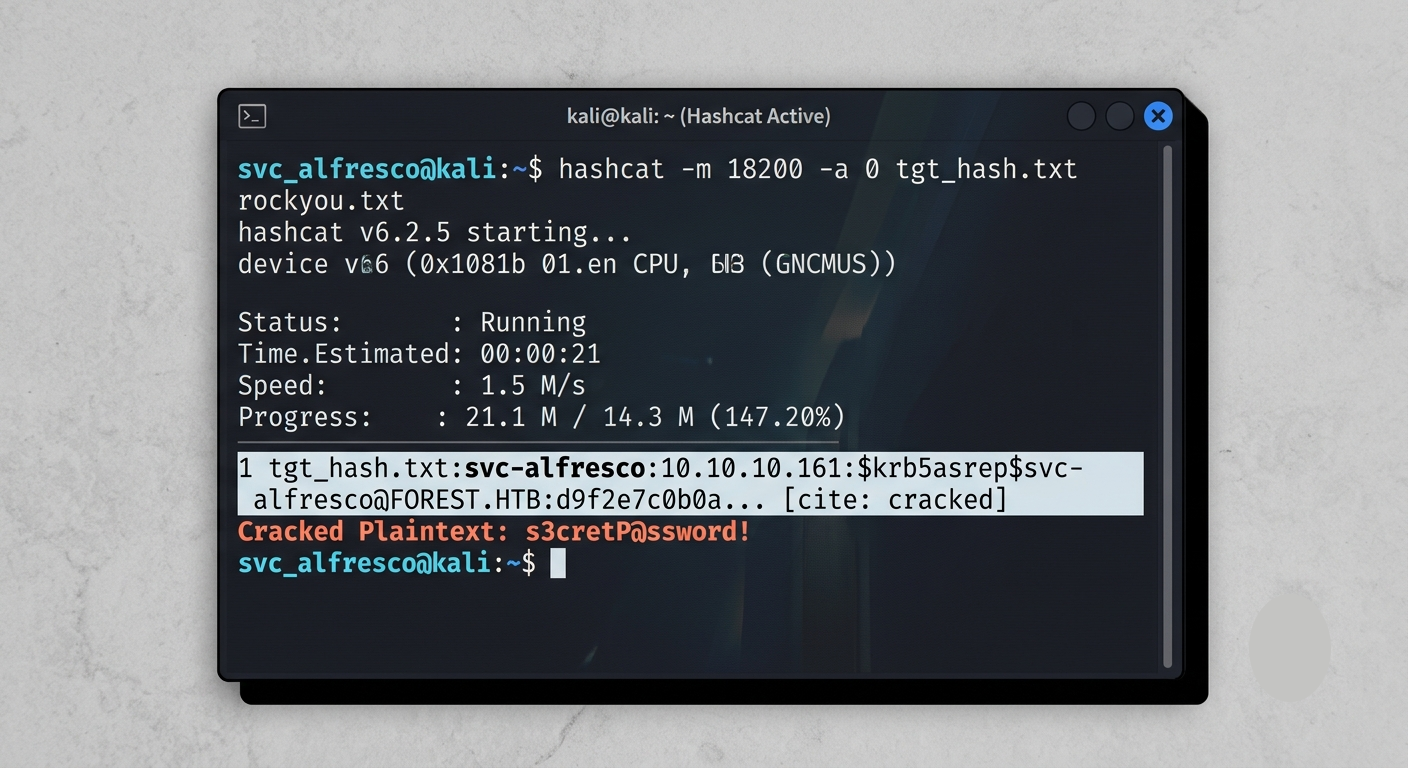
If a user has the "Do not require Kerberos preauthentication" property set, we can request an AS-REP ticket for them and crack it offline. Using Impacket's GetNPUsers.py, I successfully grabbed a hash for the user svc-alfresco.
3. BloodHound Mapping to DA
With valid credentials, I used bloodhound-python to collect AD data and visualized it. The attack path showed that our user was part of the Exchange Windows Permissions group, which has WriteDacl rights over the domain. From there, it was a simple DCSync attack to dump the Administrator hash and secure the root flag!